Every change checked, authorized and on the record
Entries are checked against your master data before they are written, roles decide access down to the row, and your business data stays in your platform.
On this page
Validated before it is written
Checked against your own master data
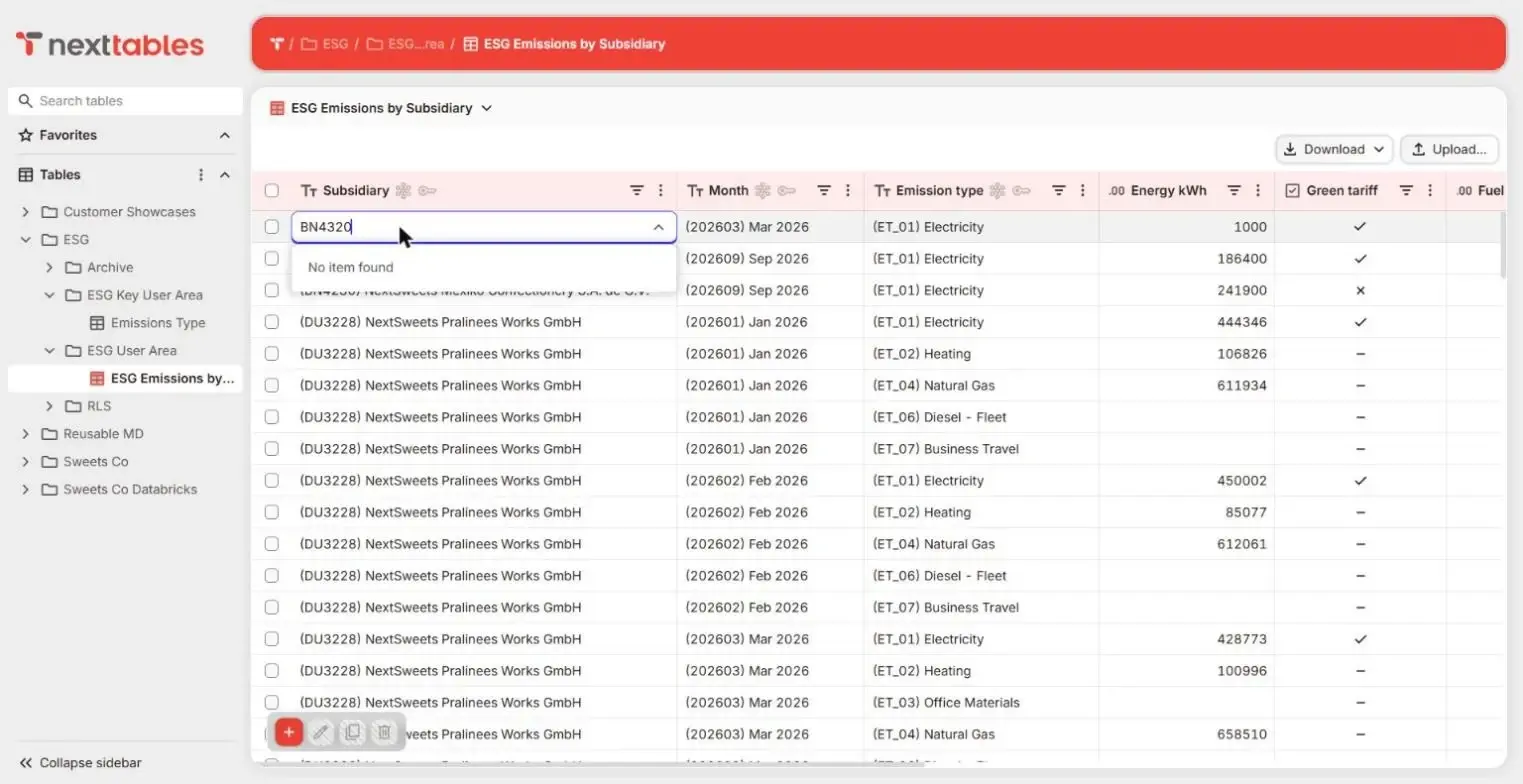
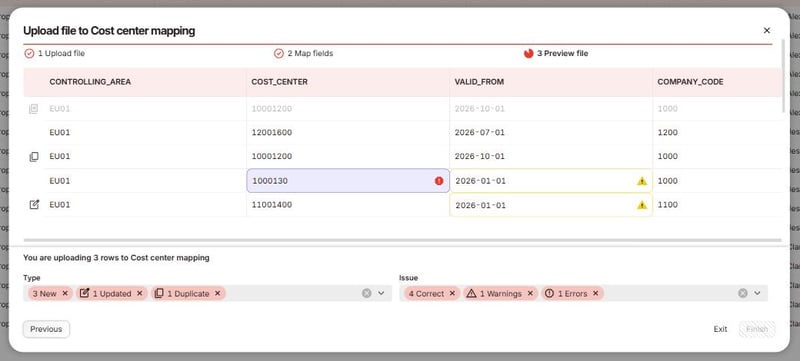
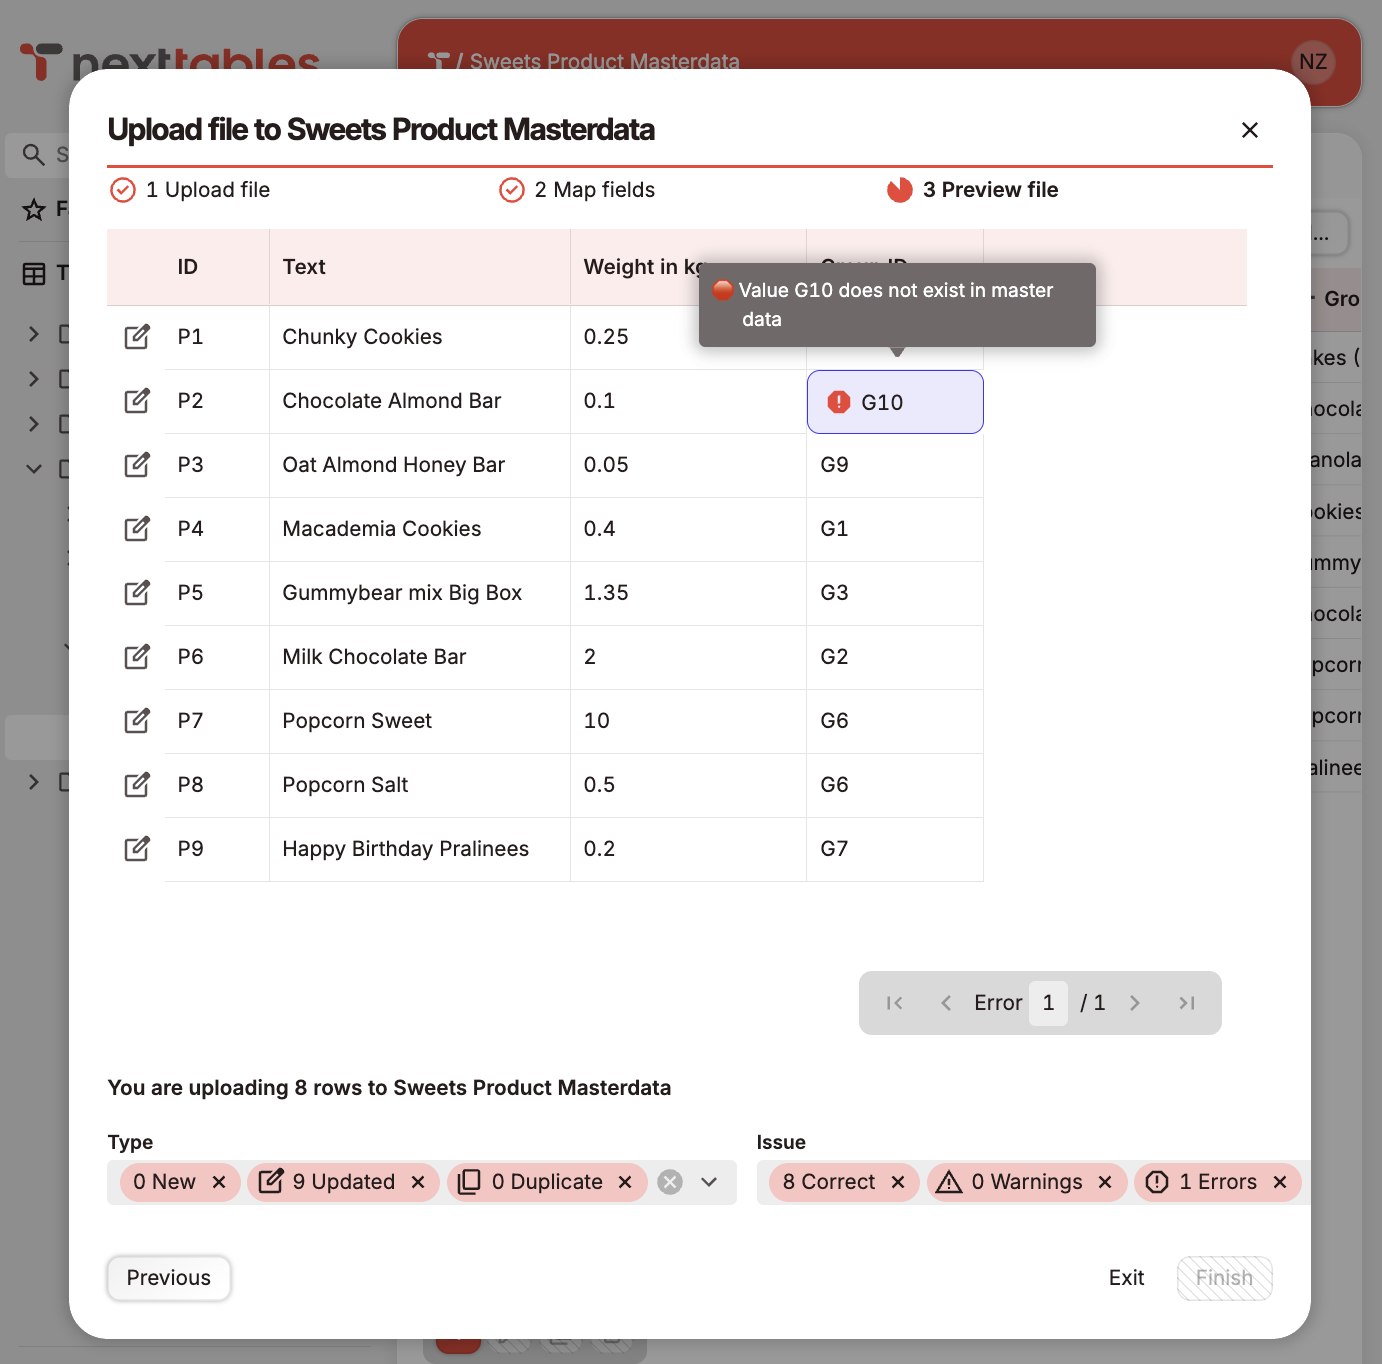
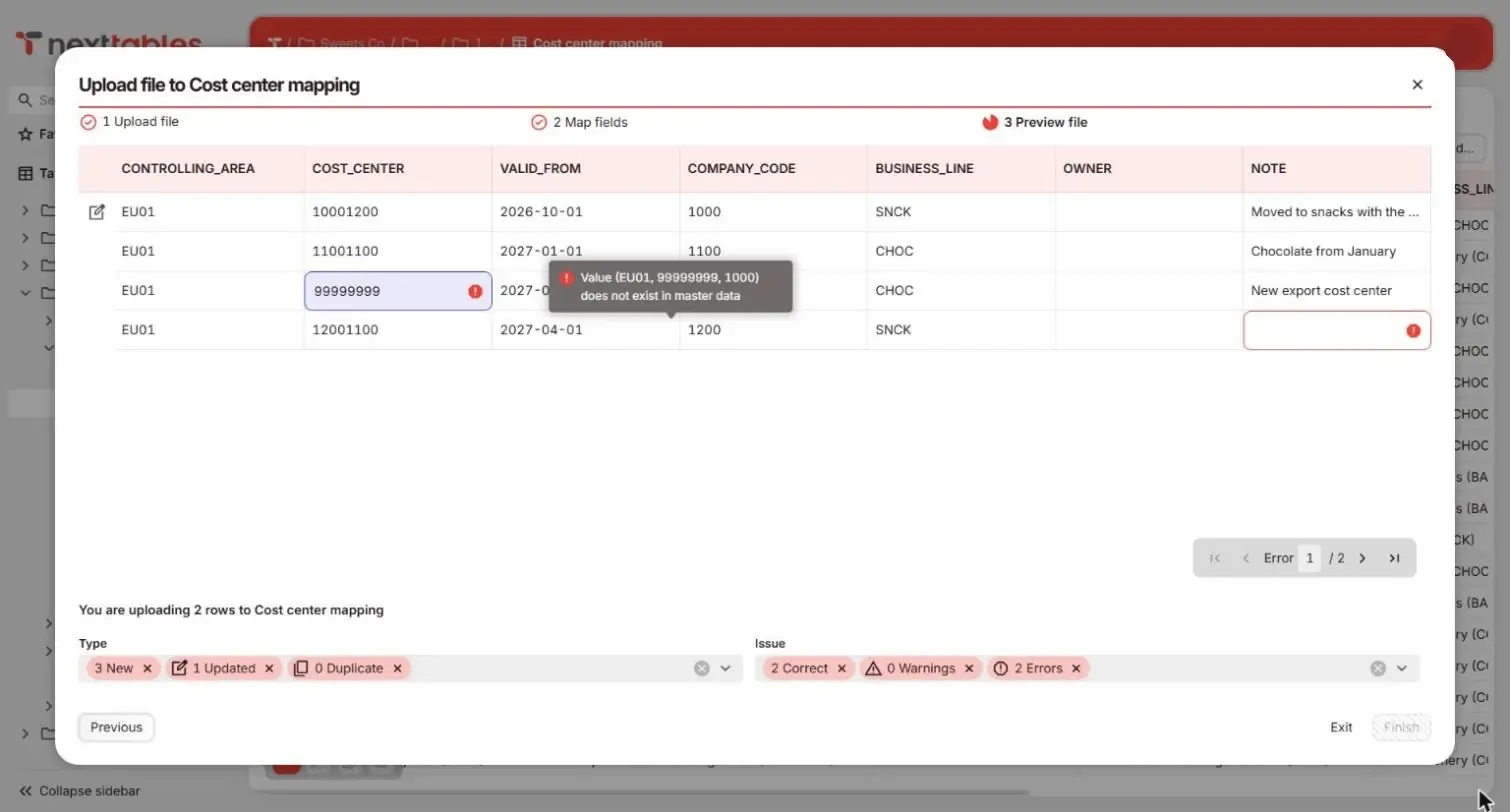
A master data object reads a table, a view or a remote table in your platform, or in another connected one. In this upload of cost center mappings, cost center 99999999 is refused with the exact key that failed: “Value (EU01, 99999999, 1000) does not exist in master data”.
Six checks and rules, and where each one is set
Swipe the table sideways to read each row in full.
| Check or rule | Set in | Example |
|---|---|---|
| Master data | Field definition | The cost center (EU01, 10001400, 1000) must exist in your master data |
| Unique key | Table key | Each combination of controlling area, cost center and valid-from date appears once |
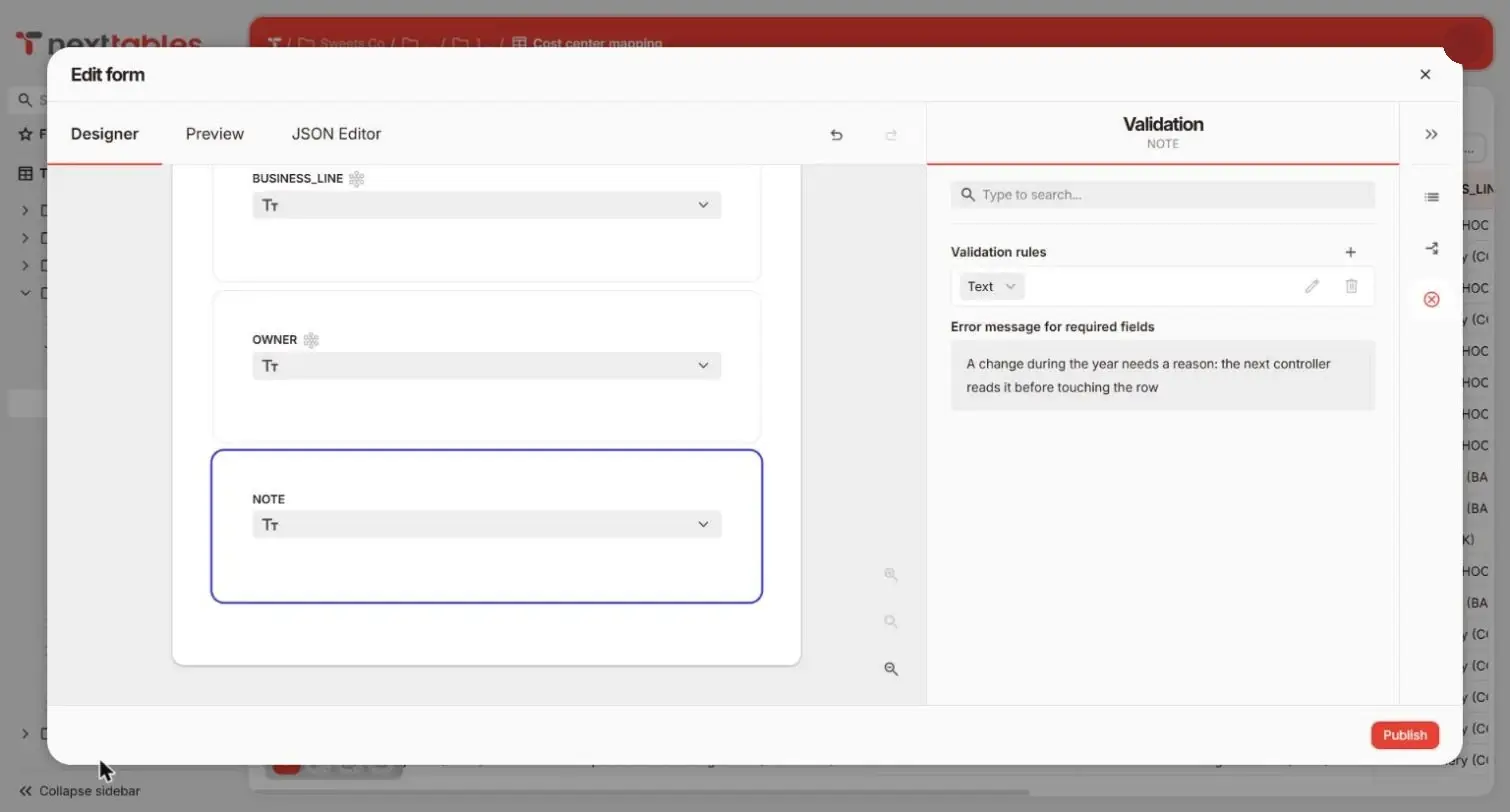
| Required if | Form condition | A note becomes required when a mapping starts during the year |
| Text | Validation rule | A comment between 10 and 500 characters |
| Regex | Validation rule | An order number in the pattern PO-123456 |
| Expression | Validation rule | A discount between 0 and 30 percent |
One rule on every entry path
A rule is configured once and applies wherever data is written: the form, inline editing in the grid, file imports, API writes and an AI assistant through the NextTables MCP server, with the same message in each. The upload above refuses the April mapping without a note, just as the form would.
Uploads are checked row by row
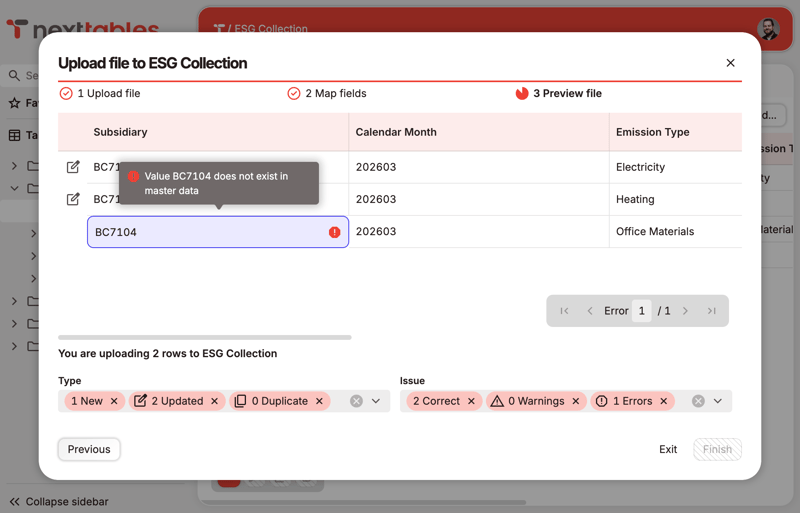
A file goes through the same rules as a keyed entry. The preview lists every row with its outcome and reason, and Finish stays locked while a row in error remains.
Your own validation code, for checks across rows and tables
Some checks need more than one value to decide. With pro-code validation, your developers write that logic as code, with read access to other tables in your platform. NextTables runs it on every entry path, and the person entering the value reads its message at the field, as with every other rule.
Coming SoonChecks it opens up
- Allocation shares that add up to 100 percent for each cost center
- A limit kept in another table, such as a credit limit per customer
- A valid-from date that follows the previous version of the same key
- One active mapping per cost center on any given day
Four layers decide who may change what
Roles: what a person may do, and where
A role is granted on a folder and inherited by its subfolders, with read, write, create and delete rights. Most tenants need three archetypes: reader, editor for the people who maintain data every day, and key user for the smaller group who may also create and change tables.
Row-level security: which rows, for which personEnterprise
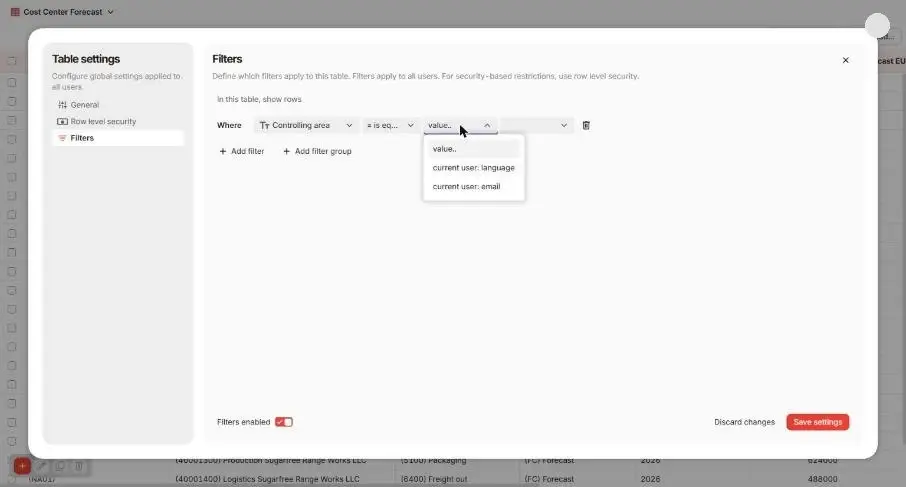
A row-level security object matches the signed-in user against a control table and decides which rows they may read and, separately, which they may write. The control table can be one you already maintain in the platform, read through the connection, or one maintained in NextTables by the people accountable for it.
Folders, the security backbone
Folders mirror your data domains, for example finance, HR and supply chain, and they are the inheritance boundary for everything above them. Restricted areas sit as subfolders inside a domain. Many customers use top-level folders as environment roots for development, test and production.
Connection scoping
A connection to a sensitive source is mapped to the folders allowed to build on it, so an application in a marketing folder stays out of the HR schema whatever its roles say. Master data objects built on a connection inherit that scope. Widening a scope is itself a site-level permission.
Row-level rules apply at the field
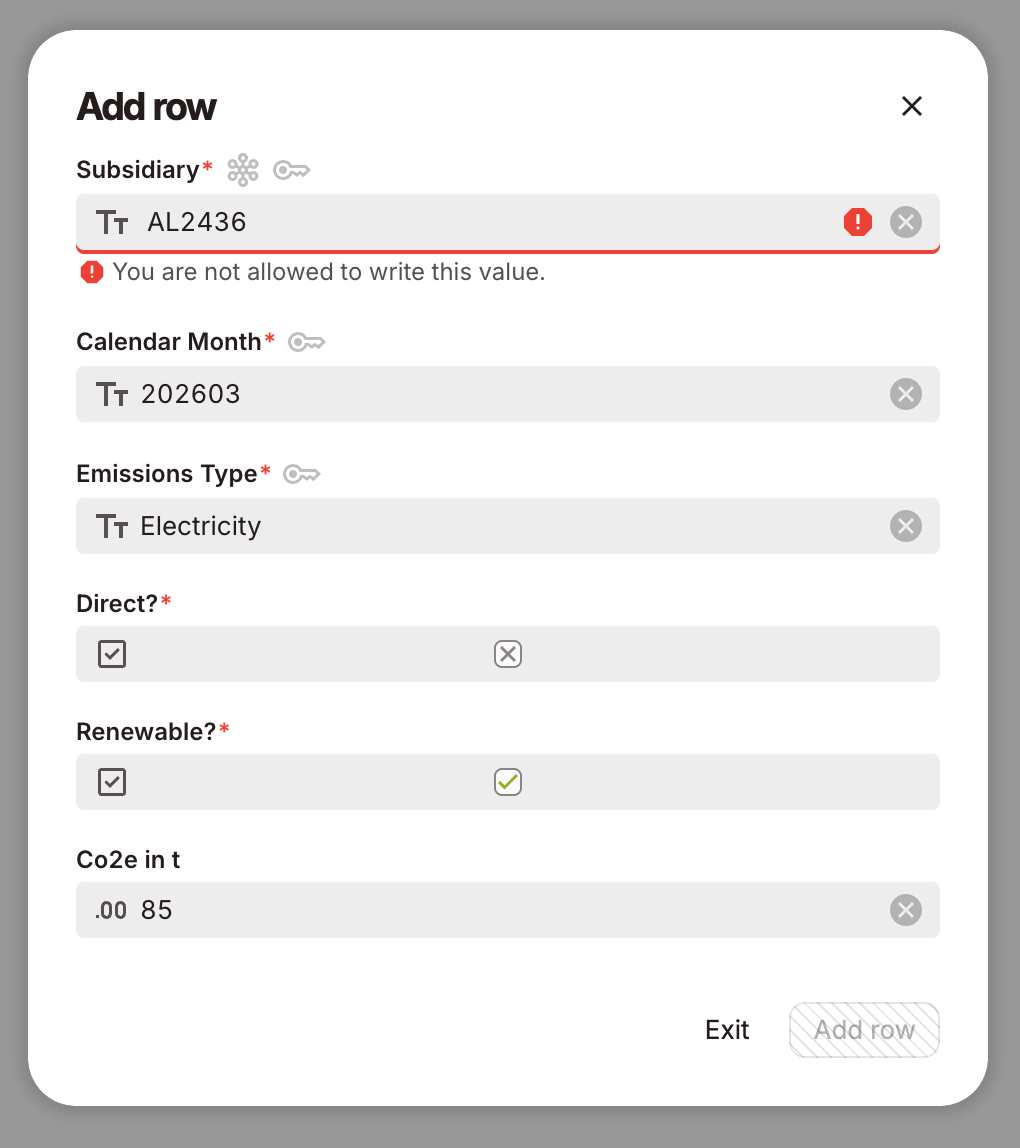
A person who enters a value outside their rows is told at the field, before anything is written. The same rule applies in the grid, in a form, by upload and through the API, and read and write access are decided separately.
%20with%20Microsoft%20and%20Google/Login%20Settings%20in%20NextTables.png?width=1303&height=902&name=Login%20Settings%20in%20NextTables.png)
Sign-in through your identity provider
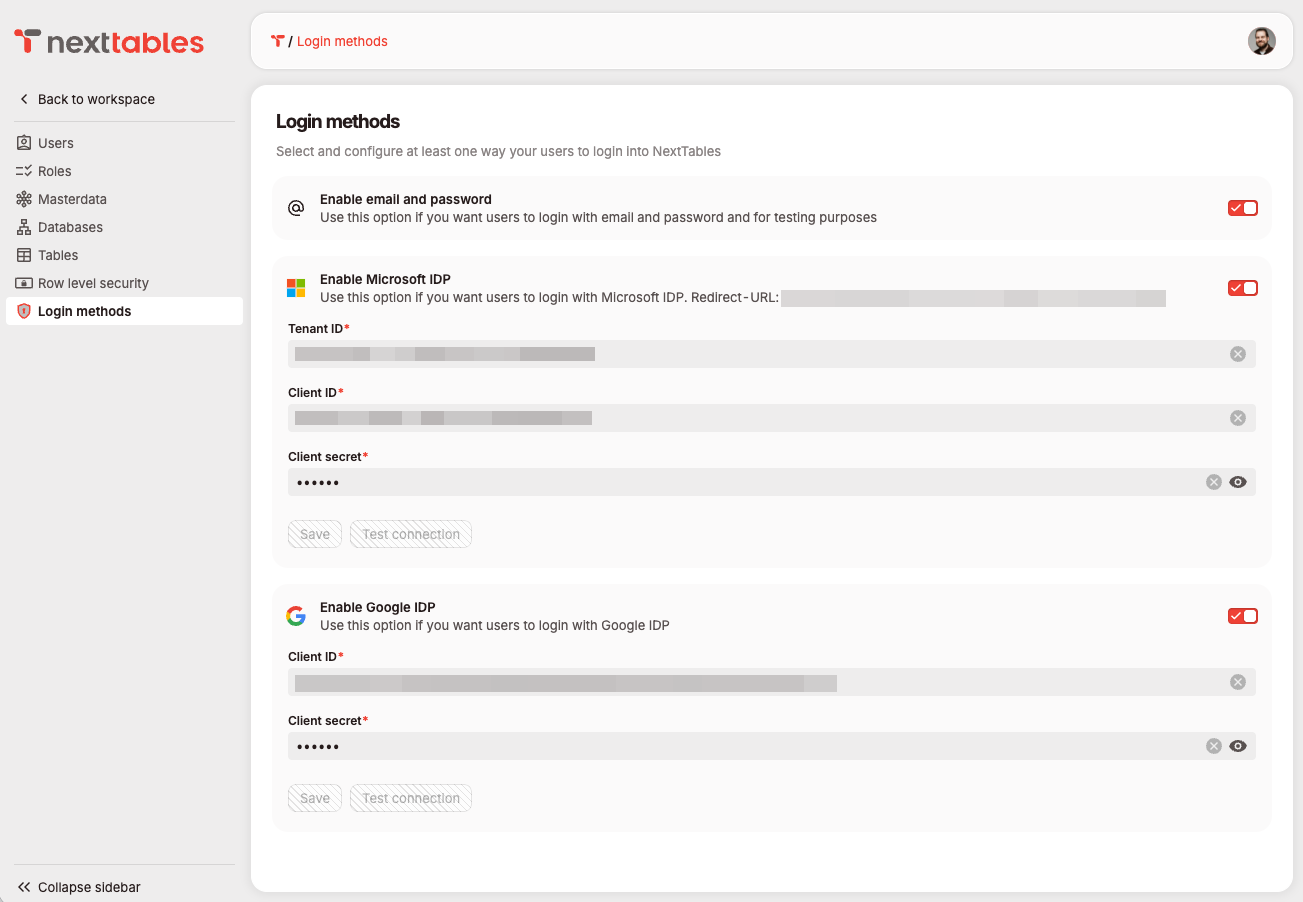
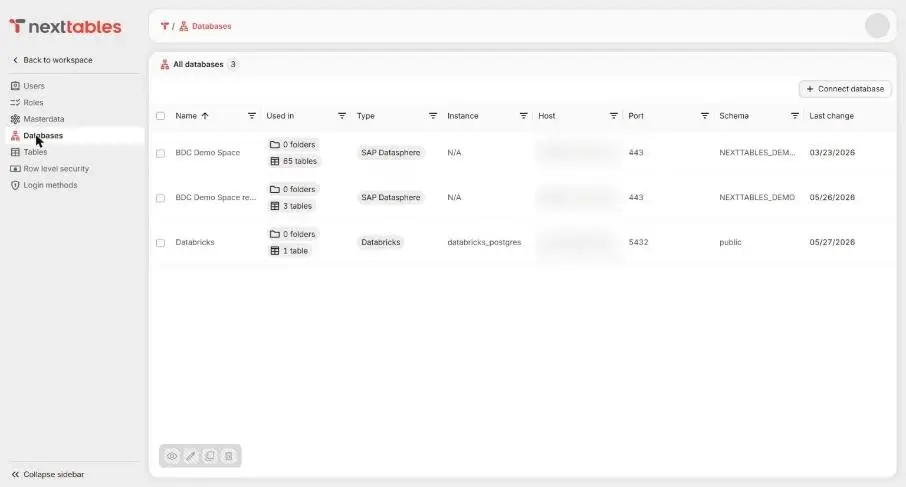
People sign in through your identity provider, Microsoft Entra ID or Google Workspace, and are authorized inside NextTables. The platform is reached through one technical connection user per schema, so maintenance-only users stay outside the platform's user management and licensing.
How the layers land on each platform: SAP Business Data Cloud (one Open SQL schema per space) and Databricks (one login role per Lakebase schema).
Platform accounts stay with the people who need them
Connections scoped by your administrator
Each connection points at the schema an administrator chose, and folders decide who may build on it. The platform's user management and licensing stay with the people who work on the platform itself, while reports read directly on the platform keep their own accounts.
An audit log of every change, stored in your own platform
Data history, set per table
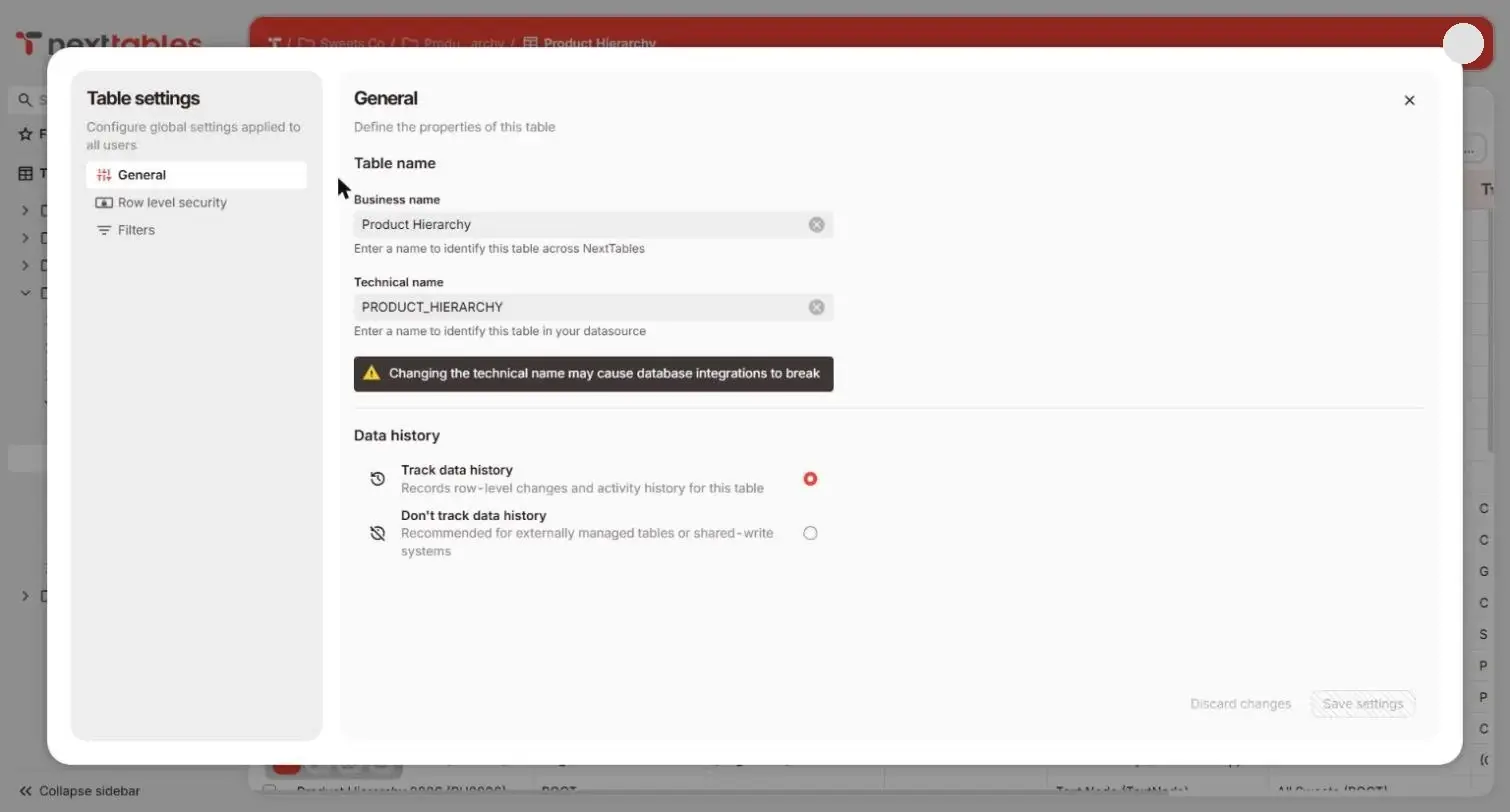
Data history is on for every new table, and administrators can switch it off per table in its settings.
The audit log is part of the Enterprise edition; the pricing page lists what each edition includes.
What one entry in the log holds
Swipe the table sideways to read each row in full.
| Table | Row | Column | New value | Changed by | Changed at |
|---|---|---|---|---|---|
| Cost center mapping | EU01 · 10001400 · 1000 | Note | Moved to logistics in April | controller@yourcompany.com | 2026-10-28 14:12 |
A change is made
It happens in the grid, in a form, by upload, through the API or from an AI assistant through the MCP server, by a signed-in person under their role.
It is validated
It is checked against your master data and your rules. Invalid values stop at the field, so only validated values reach the log and the platform.
It is written
It goes into your platform through the connection your administrator scoped, and only there.
It is recorded
The audit log row lands next to the data: who made the change, the table, the row, the changed column, its new value and the time.
Full audit trail
Coming Soon
The change history of a row, in the product interface, built on the same audit log that is on the record today.
Approval workflows
Coming Soon
For sensitive updates, edits are proposed, reviewed, and only then written, for people and for agent-driven changes alike. The decision becomes part of the record.
Safe rollback
Coming Soon
Any change can be reverted to its previous value by an authorized user, with the rollback itself recorded alongside the original change.
Your business data stays in your platform
One storage location
The tables, the views and every row live in SAP Business Data Cloud, Databricks or PostgreSQL. Reporting reads them the way it does today.
Live connections, in real time
Reads and writes go through the platform's own interface in real time. A maintained value is available in every dashboard at once.
A clean exit
Switch the connection off and the schema, the tables, the views and the data are exactly as they were. Your configuration can travel with you too, through the same export used for promotion. Coming Soon
Security and data residency
| Concern | How it is handled |
|---|---|
| Hosting | NextTables runs as a managed SaaS application on Microsoft Azure in the EU region Belgium Central, with a dedicated metadata database per tenant. Additional hosting regions follow for specific data residency requirements. Coming Soon |
| Encryption | Encryption at rest and in transit for every tenant. |
| Backups and recovery | Automated backups and disaster recovery for the tenant's configuration; your business data stays inside your platform. |
| Identity | Sign-in with Microsoft Entra ID, Google or email and password. With sign-in through your identity provider, leaving the company removes the access. |
| Data processing | A published privacy policy and a GDPR Article 28 data processing agreement. |
| Platform access | One technical connection user per schema, scoped to that schema, with the IP address shown in the connection dialog for your allowlist. Rotating a password is one value in one field. |
| Support and releases | An enterprise support model with one named path for your team, and a monthly release cycle, 30-plus releases and counting. |
Frequently asked questions
In NextTables, per application, against the master data tables the app is connected to. Every rule runs at the point of entry, ahead of the write, on every channel that writes data.
Yes. A row-level security object can read a control table in your platform through the connection, so one source of truth serves the platform's own access controls and NextTables alike.
Inside your enterprise data platform, as a regular table next to the data, for every table that tracks its data history. It can be queried with your existing platform tools today; a full audit trail in the product interface is on the roadmap.
The technical connection user, because that is what a database connection is. What changed through NextTables, who changed it and when, is in the NextTables audit log next to the data.
One sign-in per person, through your identity provider; the platform is reached through one technical user per schema that your administrator creates.
It stays where it has been the whole time: in your platform. Switch off the connection and the schema, the tables, the views and every row remain as they are.
Bring your security review
Take the deck to the review first, or spend half an hour with us on your access model, your control tables and your audit requirements.